
Business
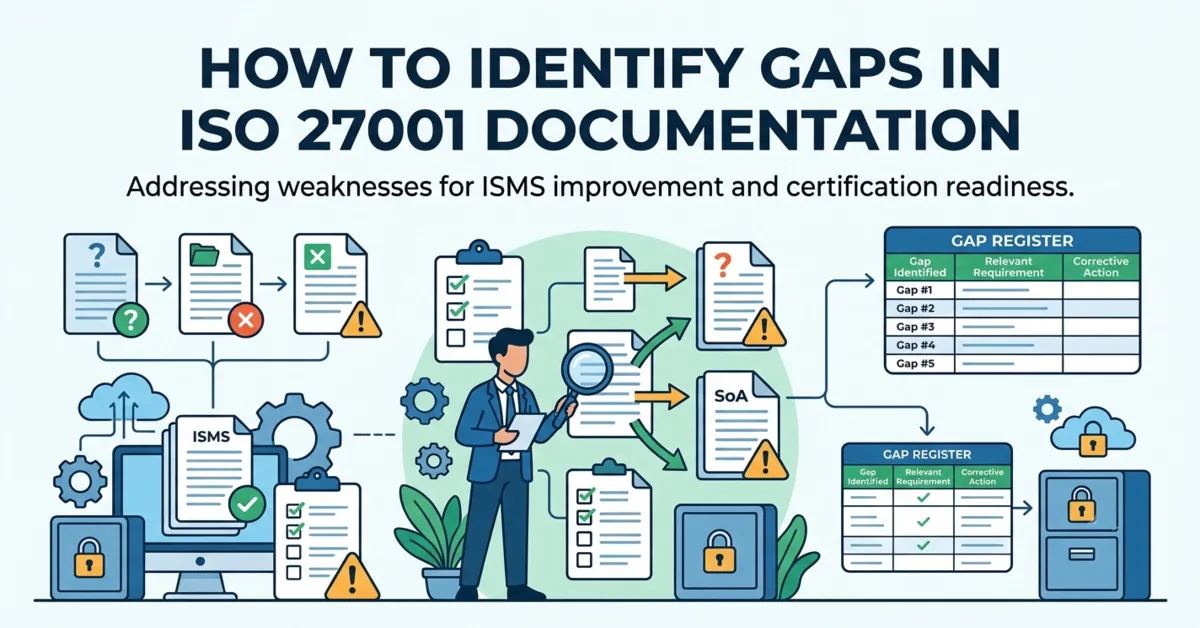
How to Identify Gaps in ISO 27001 Documentation
An Information Security Management System (ISMS) relies on documented information to manage security risks, responsibili

An Information Security Management System (ISMS) relies on documented information to manage security risks, responsibili
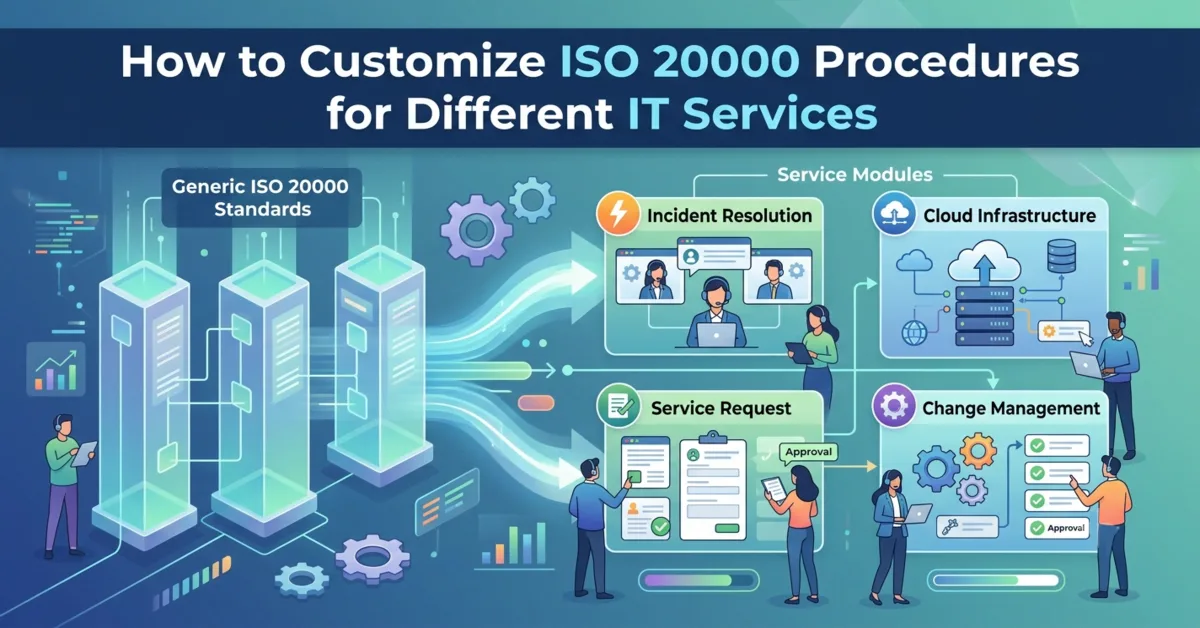
IT service providers manage activities such as incident resolution, system maintenance, service requests, network manage
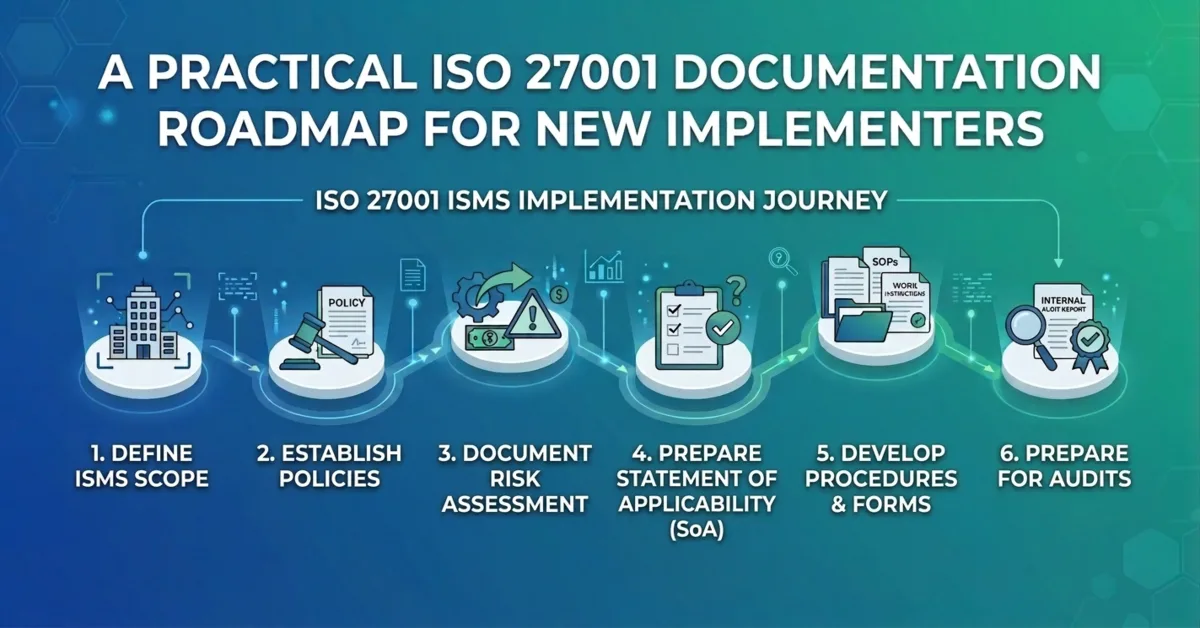
Starting an Information Security Management System (ISMS) can feel complicated, especially when an organization is prepa
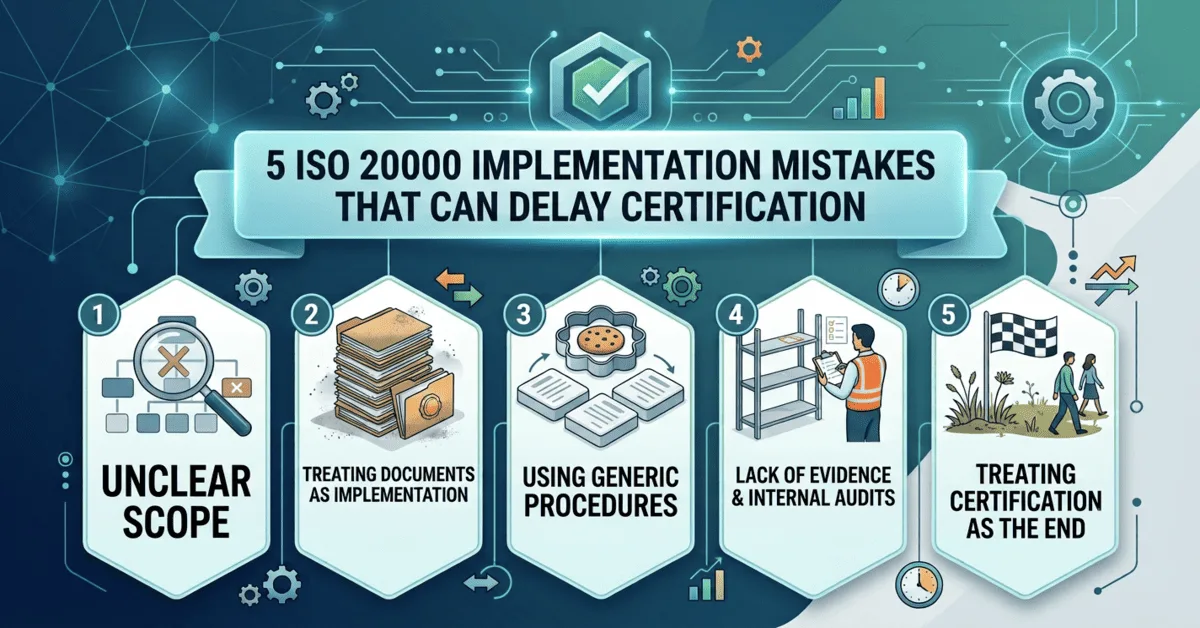
ISO 20000 implementation can become time-consuming when organizations overlook planning and focus mainly on preparing do
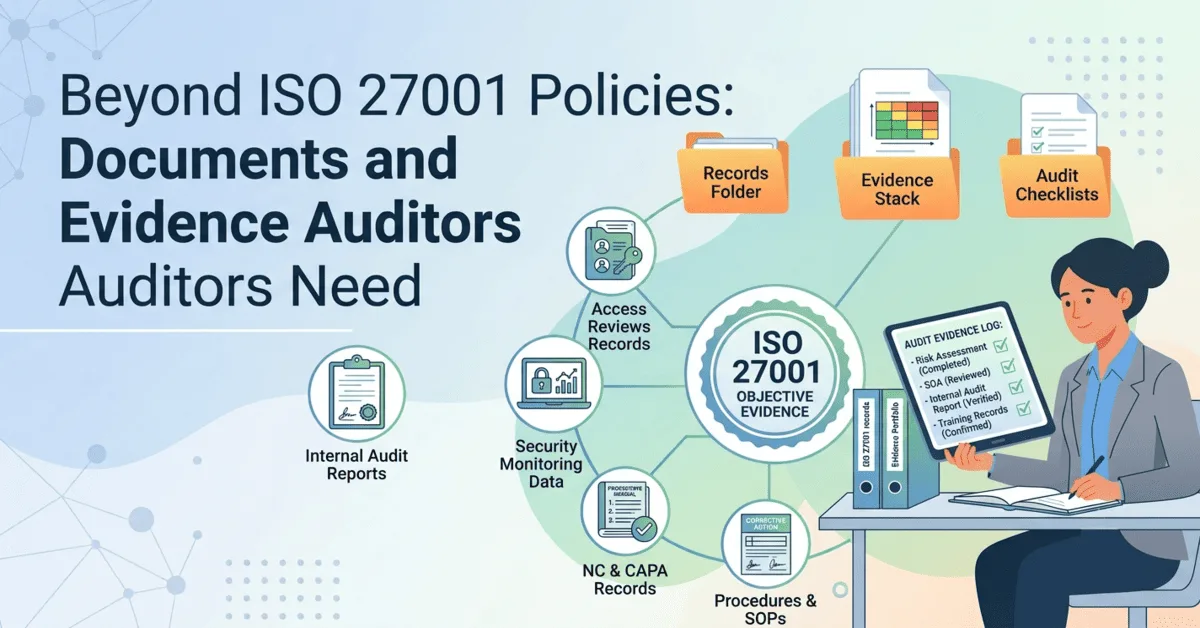
An ISO 27001 audit is not simply a review of whether an organization has an information security policy. Auditors need t
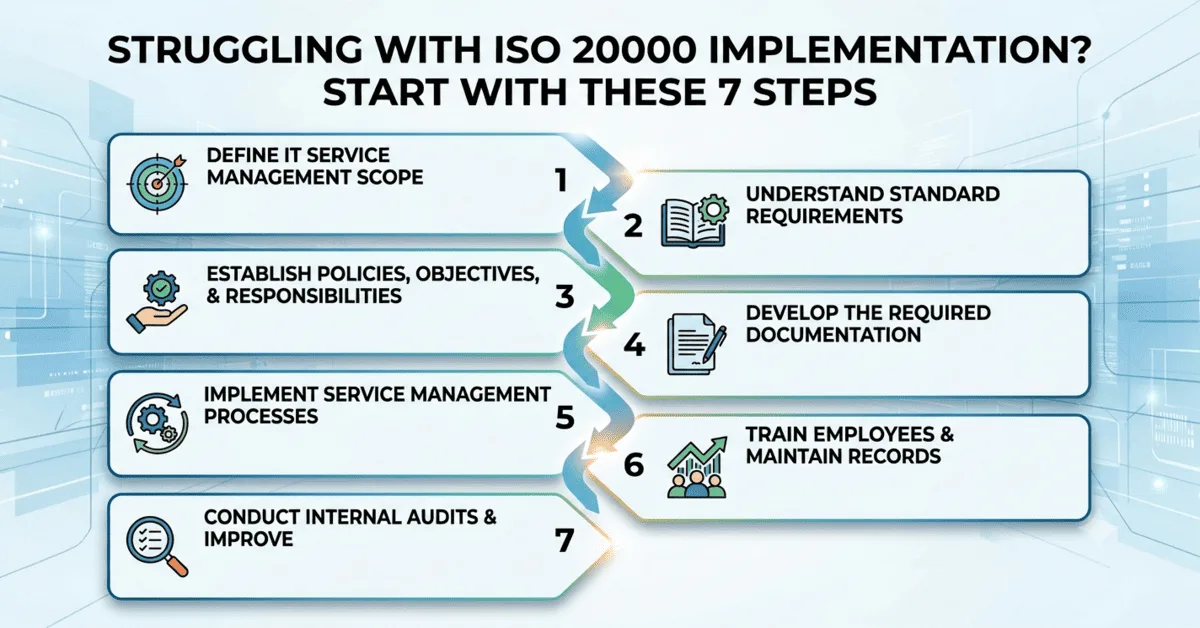
Implementing an ISO 20000 service management system can seem complicated when an organization is unsure where to begin.
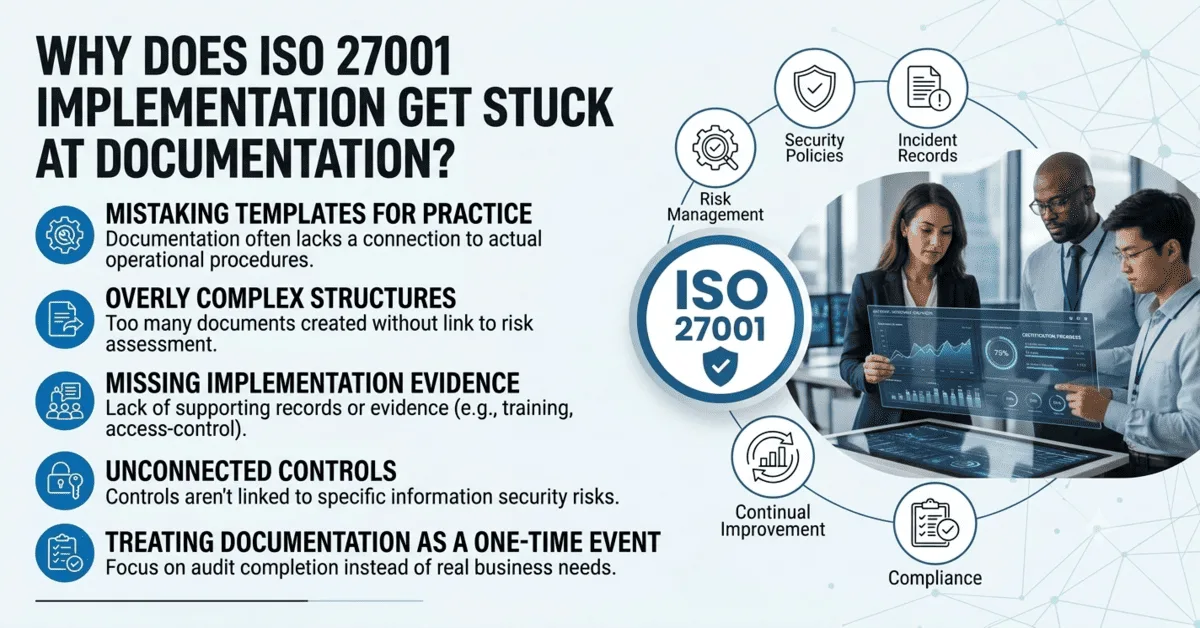
Many organizations begin ISO 27001 implementation with a clear goal: strengthen information security, manage cybersecuri
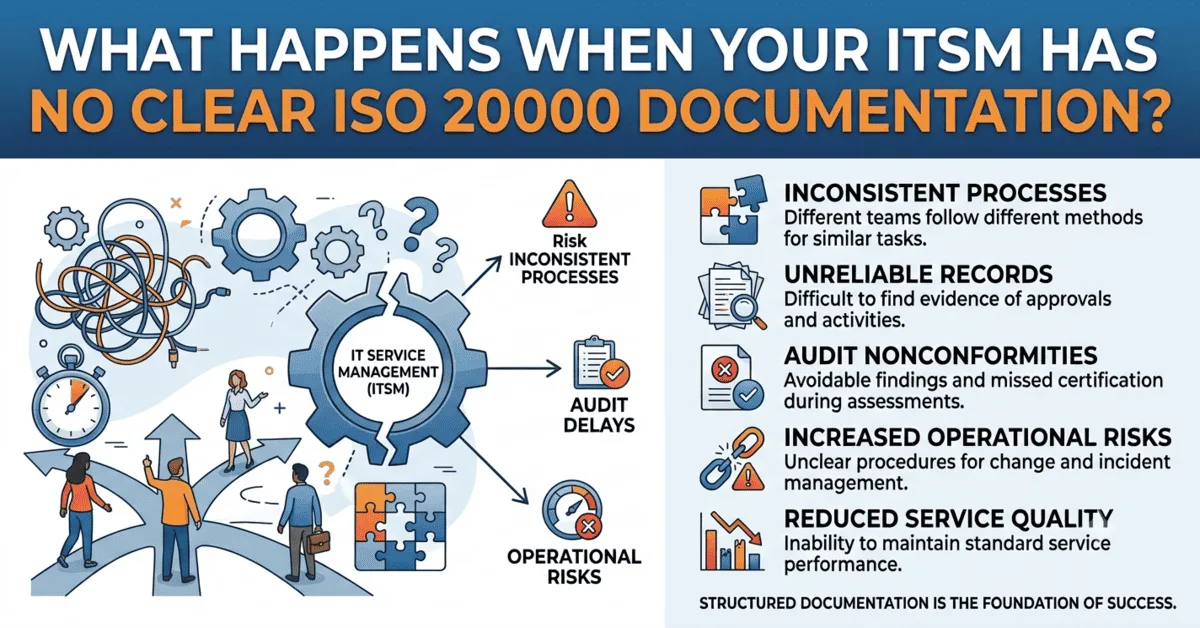
Many organizations devote a lot of effort to upgrading their IT services, but still find it challenging to succeed becau
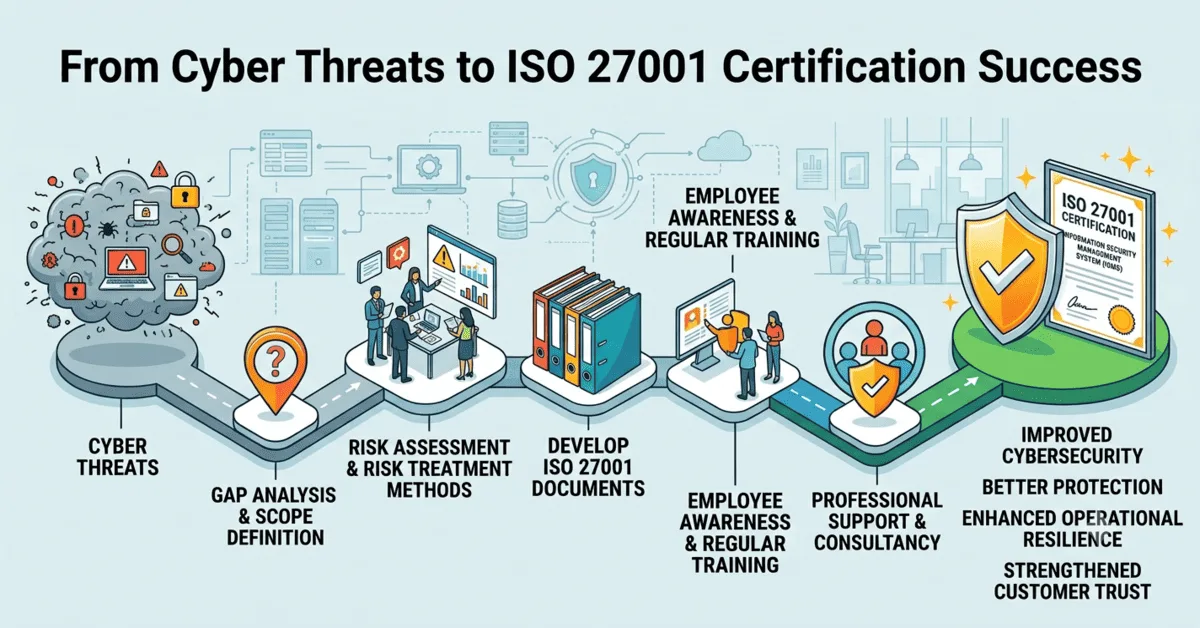
IntroductionCyber threats have become one of the biggest challenges for modern organizations. Data breaches, ransomware