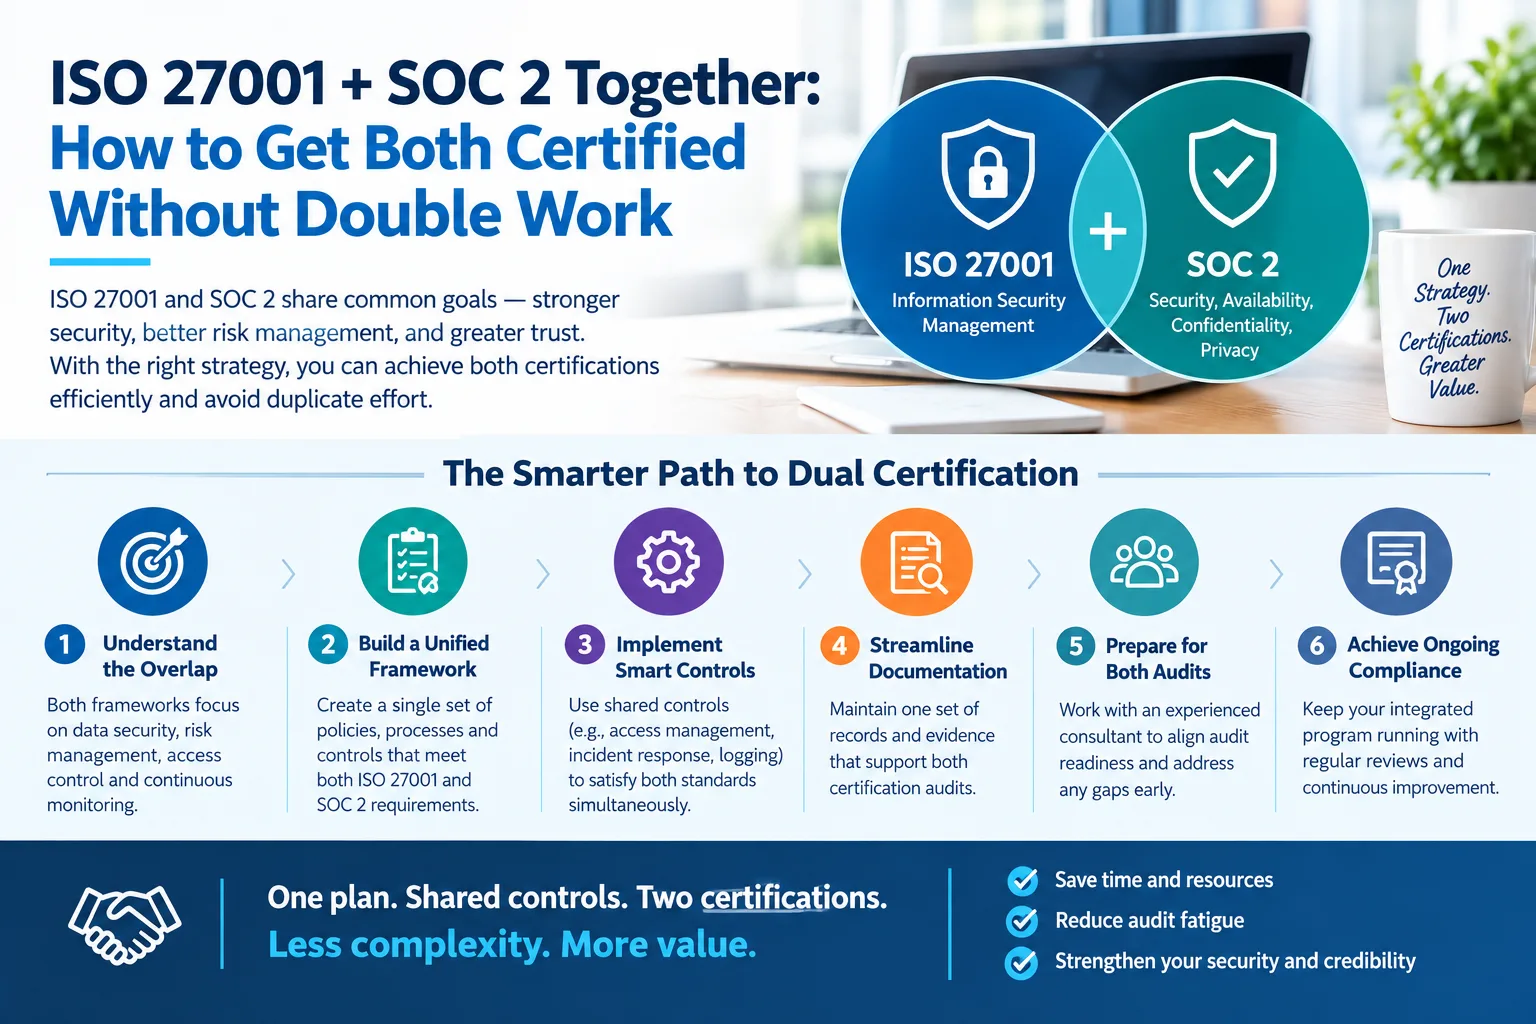
US buyers often ask for SOC 2; global buyers ask for ISO 27001. Both prove you protect data, but in different formats. Running two programs means double policies and double evidence. You can avoid that by building one program that satisfies both, often with help from ISO 27001 consulting services that map controls once and reuse them.
Why Companies Pursue Both Standards
SOC 2 is an AICPA attestation report against Trust Services Criteria, issued by a CPA firm and refreshed annually. ISO 27001 is an international standard for an Information Security Management System, or ISMS, issued as a certificate with annual surveillance and recertification every three years.
SOC 2 dominates North American SaaS procurement. ISO 27001 is recognized worldwide and often required in EU and APAC tenders. Having both reduces sales friction.
What Makes ISO 27001 And SOC 2 Different And Similar
Where The Two Frameworks Overlap
Operational controls overlap 70 to 80 percent. Both require:
- Access control: least privilege, joiner mover leaver, MFA, periodic reviews
- Risk assessment: registration, treatment, approvals
- Incident response: detection, plan, postmortems
- Vendor management: inventory, due diligence, contracts
- Change management: review, testing, approvals
- Logging, monitoring, vulnerability management, training
Build these once with owners and dates and you cover most of both audits.
Where They Diverge
ISO 27001:2022 has clauses 4 to 10 plus 93 Annex A controls across organizational, people, physical, and technological themes. It requires scope, leadership, objectives, internal audits, management reviews, and continual improvement.
SOC 2 has Security Common Criteria CC1 to CC9 as required, plus optional Availability, Confidentiality, Processing Integrity, and Privacy. Type 1 checks design at a point in time. Type 2 checks effectiveness over 3 to 12 months. ISO gives a certificate. SOC 2 gives a report.
How To Build One Control Set For Both Audits
Start With A Unified Risk Assessment
Make one risk register with assets, threats, vulnerabilities, controls, inherent and residual risk, owners, and dates. This satisfies ISO clause 6.1 and SOC 2 CC3. One approved register anchors both.
Map Controls Once To Both Standards
Create a matrix with Annex A control, ISO clause, SOC 2 criterion, control statement, owner, and evidence source. Use AICPA mapping as a start and update for 2022.
Example: CC6.1 maps to A 5.15, 5.17, and 8.5. CC7.2 maps to A 8.16 and A 8.7. Collect evidence once: IdP logs for MFA, tickets for access reviews, HR exports, training completion, pentest reports, SIEM alerts, and change tickets. Tag each file with control IDs and a timestamp.
Step-by-Step Path To Dual Certification Without Double Work
Step 1: Define A Common Scope
Write an ISMS scope statement and SOC 2 system description covering the same product, infrastructure, and teams where possible. A narrow scope moves faster.
Step 2: Create One Evidence Model
For each control, define what good evidence looks like, where it lives, how often you collect it, and who owns it. Store in one repository with timestamps. Consistent collection stops duplicate screenshots.
Step 3: Run Combined Readiness Checks
Do one gap analysis against both standards. Verify policies match practice. Check the internal audit and management review for ISO and operating history for SOC 2. Fix gaps once.
Step 4: Coordinate Audit Timing
Parallel means ISO Stage 2 and SOC 2 Type 2 in the same quarter using the same package. Sequential means SOC 2 Type 1 for sales, then ISO, then Type 2. Start with the artifact your largest deals need.
Putting It All Together For Efficient Certification
One risk register, one control library, one evidence repository, and one calendar. That reduces work and makes yearly refreshes easier.
If you want a faster path, Sync Resource helps align current practices with certification needs. Based in Alpharetta, Georgia, the firm has supported 340-plus clients since 2009 with gap analysis, documentation, implementation, and audit support, with most clients audit-ready in 30 to 90 days. Working with experienced ISO 27001 consulting services shortens the path to both without adding overhead.
FAQs
Can You Get ISO 27001 And SOC 2 At The Same Time?
Yes. Build one ISMS, map Annex A to Trust Services Criteria, and collect evidence once. You still complete two audits, but prep is shared.
How Much Overlap Exists Between ISO 27001 And SOC 2?
Most teams see 70 to 80 percent overlap in access, risk, incident response, vendor oversight, and change management. ISO adds ISMS requirements; SOC 2 can add availability and privacy.
Which Should You Do First, ISO 27001 Or SOC 2?
Start with what buyers ask for most. North American SaaS often needs SOC 2 Type 1 fast. Global buyers need ISO 27001 first. Map to the other from day one.
Do You Need Separate Evidence Sets For Each Audit?
No. Define owner, frequency, source, and retention for each control. Tag artifacts to both frameworks. Some items are unique, like management review minutes for ISO or system description for SOC 2, but most can be reused.
How Long Does Dual Certification Take?
Readiness can take 2 to 4 months plus 3 to 12 months for the SOC 2 Type 2 period. ISO Stage 1 and Stage 2 follow readiness. One evidence set prevents extending the timeline.